NorthLine Human Risk Simulator
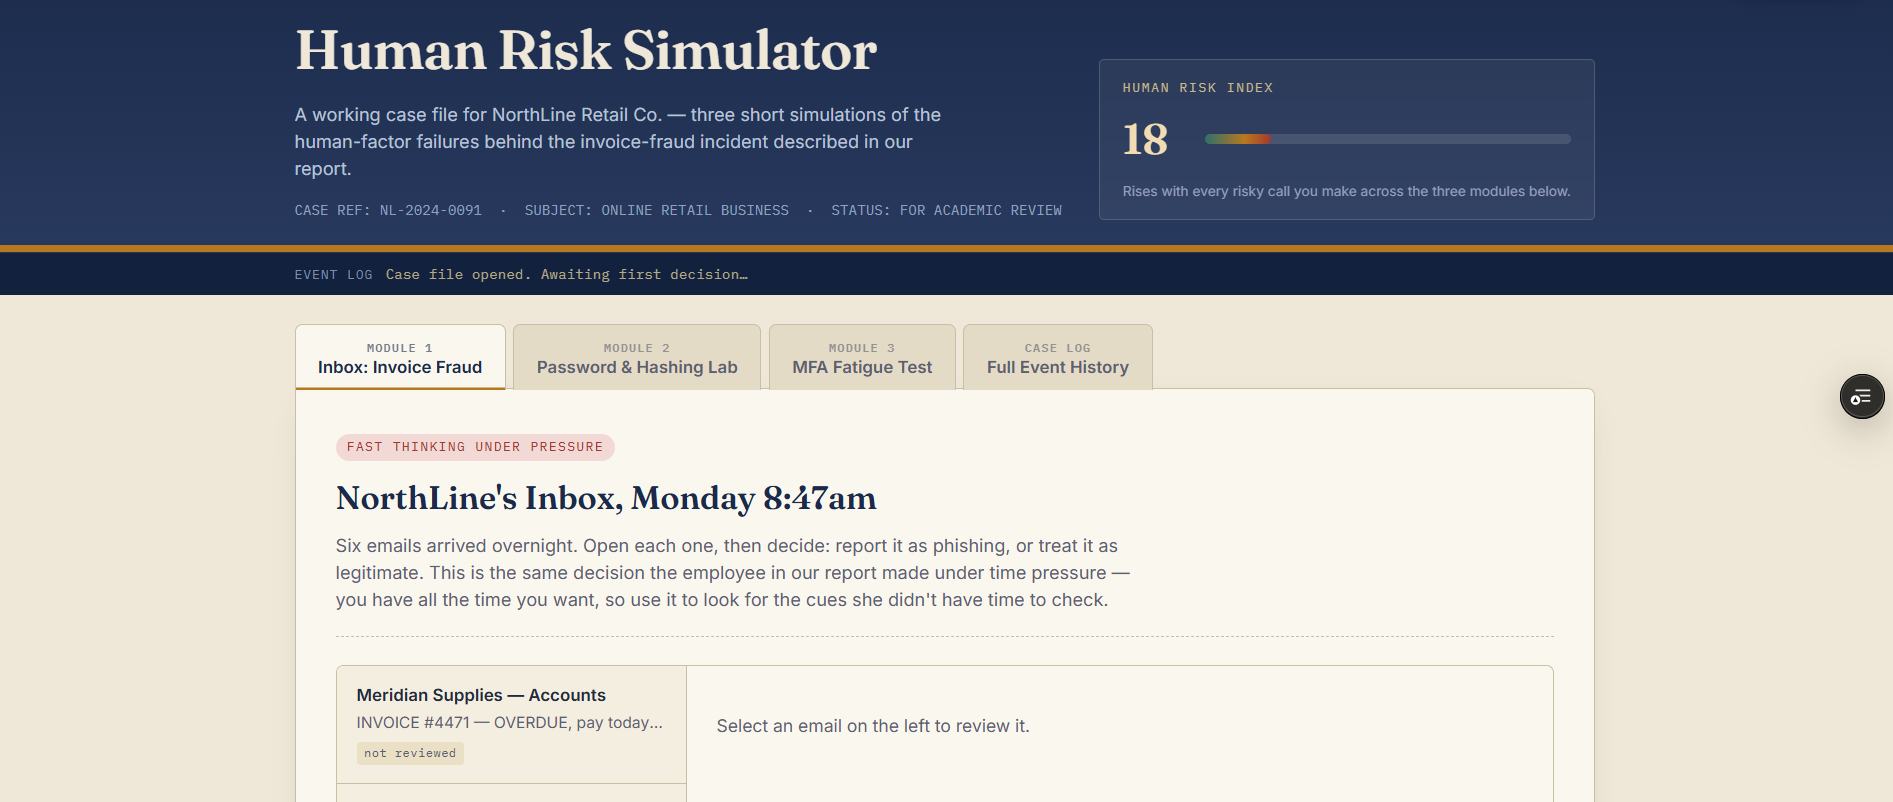
NorthLine is a single-page web application built for a unit case study, simulating three real-world human-factor security failures for a fictional retail business: a phishing-detection trainer, a password and hashing lab, and an MFA-fatigue simulator. Every decision a user makes across the three exercises feeds into a running "Human Risk Index," turning the simulation into a coherent narrative about how everyday security lapses compound.
Key features
- Phishing detection trainer, six-email inbox exercise with cue-based feedback
- Password & hashing lab, live entropy scoring and salted-hash demonstration
- MFA fatigue simulator, timed approval prompts modelling notification-fatigue attacks
- Session event log, tracks every decision against a running "Human Risk Index"
A standout technical detail: rather than calling the browser's built-in Web Crypto API, the SHA-256 hashing used in the password lab was implemented by hand directly from the FIPS 180-4 specification, including message padding, the 64-round compression function, and the standard round constants, then verified byte-for-byte against Node.js's native crypto module across multiple test vectors.
The entire application is a zero-dependency, single self-contained HTML/CSS/JS file, no framework, no build step, with a light/dark theming system built entirely on CSS custom properties. It deploys via CI/CD from GitHub to Vercel, auto-redeploying on every push.
Stack: HTML5, CSS3, vanilla JavaScript · GitHub · Vercel
My role
This was a group project for a unit case study; I developed the web simulation itself, the phishing trainer, password/hashing lab, MFA-fatigue simulator, and the original SHA-256 implementation.